Top Access Control System Software for Businesses
Choosing Access Control System Software is not just a matter of comparing feature lists. It affects how employees enter, how visitors are checked in, and how access changes when roles shift. A busy office may need mobile credentials and clear entry logs. A warehouse may depend more on reliable door hardware and straightforward site management. Small details matter. A delayed permission update can create confusion at a reception desk.
Security expert Bruce Schneier offers a useful lens: “Security is a process, not a product.” His reminder applies to access control, where software works alongside people, policies, and physical doors. This guide compares business platforms by practical criteria, including credential options, user management, reporting, integrations, and support. It also considers deployment needs, from a single office to multiple locations. No system fits every building. That is worth admitting.
A polished dashboard can look convincing in a demo, yet daily tasks reveal more. Can an administrator revoke a lost credential quickly? Are access records understandable during a routine review? Do integrations match the tools a business already uses? These questions help separate useful capabilities from features that may never leave the sales presentation. The sections ahead highlight leading options and the trade-offs buyers should examine. Treat any shortlist as a starting point, not a verdict. The right choice depends on the doors, workflows, and people the software must serve.
Access Control Software Defined: Credentials, Permissions, and Audit Trails
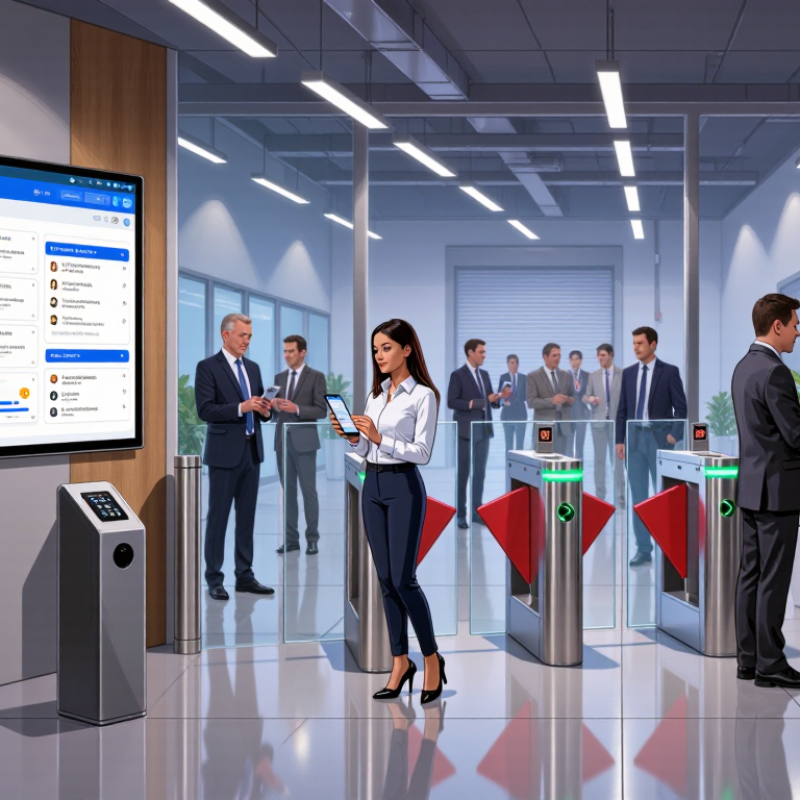
Access control software links a person’s credential to the doors or areas they can use. Credentials may be cards, mobile passes, or PINs, but each needs a clear owner and status. When someone changes roles or leaves, administrators should update or revoke access promptly. Small details matter. A misplaced card can remain active unless the process catches it.
Permissions determine who can enter specific spaces and when. A receptionist might need the lobby and office entrance, while a facilities technician may need scheduled access to equipment rooms. Use role-based rules where they fit, then review exceptions individually. That sounds tidy on paper; real teams are messier. Overly broad permissions can linger because changing them disrupts daily work, so periodic reviews need named owners and practical deadlines.
Audit trails record events such as denied entries, credential changes, and administrator actions. Useful records include a timestamp, the affected door, and the credential involved. During an incident review, this detail can clarify what happened without relying only on memory. Logs are not perfect evidence: clocks may drift, and a shared credential obscures who used it. Check time settings, restrict administrative access, and define how long records are retained. Keep the policy understandable to the people who actually manage the system.
Top Access Control System Software for Businesses - Access Control Software Defined: Credentials, Permissions, and Audit Trails
A practical overview of common access-control software capabilities, credential types, permission rules, and audit records used to manage access to business spaces.
| Capability | Common Examples | How It Works | Typical Audit Information | Operational Consideration |
|---|---|---|---|---|
| Credentials | Access cards or fobs, mobile credentials, PINs, and biometric identifiers | A credential is presented to a reader or device and checked against the access rules configured in the system. | Credential identifier, reader or door, event time, and access result, where supported | Credentials should be assigned to individual users where possible, and lost or compromised credentials should be disabled promptly. |
| Permissions | User, role, door, area, and time-based access rules | Permissions determine which people or groups may use specified access points and during which scheduled periods. | Permission changes, affected user or group, administrator account, and change time | Use the minimum access needed for each role and review permissions when job duties change. |
| Schedules | Business hours, shift windows, holidays, and temporary access periods | Schedules allow or restrict access according to configured days and times; behavior can depend on the system and door settings. | Access attempts with timestamps, including attempts outside an allowed schedule | Check time zones, holiday calendars, and schedule changes to avoid unintended access gaps or extensions. |
| Door and area management | Individual doors, entrances, floors, and grouped areas | Access points can be organized so permissions can be applied consistently to particular locations. | Door or reader identifier, event type, and access decision | Use clear, consistent names for doors and areas so administrators can interpret reports reliably. |
| Visitor access | Time-limited credentials, temporary PINs, or escorted visitor records | Temporary access can be limited by location and expiration time; the available options vary by system configuration. | Visitor or credential reference, sponsor or issuer where recorded, permitted area, and validity period | Set an end time for temporary access and follow site procedures for visitor identification and escorting. |
| Audit trails | Granted and denied access events, credential changes, and permission updates | Audit records provide a time-ordered history of selected access events and administrative actions. | Common fields include timestamp, event type, access point, credential or user reference, result, and administrator reference when applicable. | Available fields, retention periods, and export options differ. Set retention and access practices according to operational needs and applicable requirements. |
| Credential revocation | Deactivation of a lost card, departed employee credential, or expired temporary credential | An administrator disables or expires a credential so it can no longer be used under the system’s access rules. | Credential status change, administrator reference, and time of change where logged | Include revocation in offboarding and lost-credential procedures, and verify that changes reach relevant access points. |
| Reporting and review | Access-event searches, denied-entry reports, and permission reviews | Administrators filter records by factors such as date, user, door, or event type, depending on available reporting features. | Selected event details and report-generation or export information where supported | Limit report access to authorized personnel and periodically review permissions and record-handling practices. |
Note: Features, event fields, integrations, and retention settings vary by system. Confirm configuration and applicable privacy, security, and record-retention requirements before deployment.
Related Posts
-
What Is the Best Access Control Software in China?
-
Ultimate Guide to Choosing the Best Security Devices for Your Home
-
Digital Innovations in Best Access Control Security Solutions
-
Top 10 Essential Security Devices Everyone Should Consider for Home Safety
-
2026 Best Card Access Control Systems for Global Buyers
-
2026 Best Access Control System Software for Secure Solutions?